

Cyber Attack Targets Check Point, F5 BIG-IP APM, and Spark Firewalls
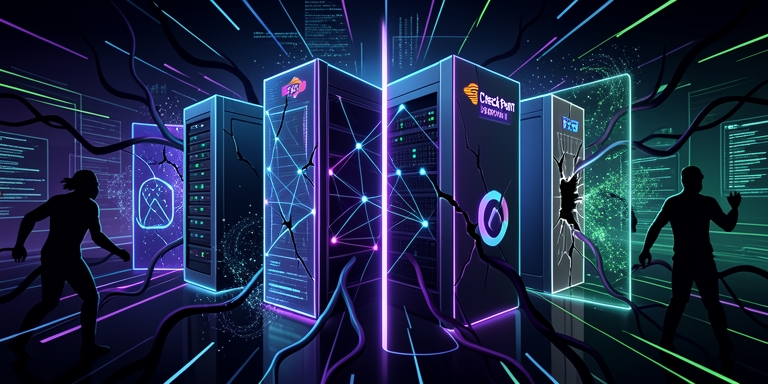
Attackers have exploited critical vulnerabilities in Check Point Management Servers, Spark firewalls, and F5 BIG-IP APM systems, according to newly disclosed security advisories.
Check Point Management Server Vulnerability
CVE-2026-93616 is a path traversal vulnerability affecting the Check Point Management web service, impacting Security Management Server, Multi-Domain Security Management Server, Log Server, and Multi-Domain Log Server. Attackers can leverage this flaw to upload and execute arbitrary code, with reports indicating that a small number of customers have already been compromised.
CVE-2026-93616 Details
Check Point provided mitigation steps, including hotfixes and indicators of compromise (IOCs) for affected systems. Organizations unable to apply updates immediately are advised to restrict Management Server access to trusted internal IP ranges.
Mitigation Steps
Check Point urged customers to install the patch immediately and monitor logs for suspicious Mobile Access activity, including unauthorized internal network scanning. Mitigation options are available for centrally managed Spark firewalls but not for locally managed ones.
Check Point Spark Firewall Vulnerability
CVE-2026-85102 targets Check Point Security Gateway systems, specifically Spark Firewalls used by small and medium-sized businesses (SMBs) and managed service providers (MSPs). Exploitation attempts began on September 12, 2026, originating from anonymization tools such as VPNs and proxies.
CVE-2026-85102 Details
The attacks utilized specific certificate subjects outlined in the vendor’s security advisory. Check Point confirmed that a separate pre-authentication remote code execution (RCE) vulnerability (CVE-2026-85102) in Check Point Spark Firewalls began facing exploitation attempts after patches were released on September 9, 2026.
Mitigation Options
Organizations unable to apply updates immediately are advised to restrict Management Server access to trusted internal IP ranges. Check Point urged customers to install the patch immediately and monitor logs for suspicious Mobile Access activity, including unauthorized internal network scanning.
Additional Vulnerabilities
In addition to Check Point flaws, two zero-day vulnerabilities were added to CISA’s Known Exploited Vulnerabilities catalog. CVE-2026-93952 affects Arista VeloCloud Orchestrator, a central management platform for SD-WAN solutions, by allowing improper input validation. CVE-2026-94127 impacts F5 Networks BIG-IP APM systems, enabling unauthenticated remote code execution if instances are configured as OAuth Authorization Servers.
Arista VeloCloud Orchestrator
Both vendors released IOCs for affected environments. Arista Networks and F5 Networks have not disclosed specific details about the zero-day attacks but provided technical indicators for affected systems.
F5 BIG-IP APM
CVE-2026-94127 impacts F5 Networks BIG-IP APM systems, enabling unauthenticated remote code execution if instances are configured as OAuth Authorization Servers. Both vendors released IOCs for affected environments.
CISA Mandate
CISA mandated that U.S. civilian federal agencies resolve all four vulnerabilities by September 25, 2026, and verify system compromises. Private sector organizations were also advised to address the flaws promptly.
Expert Commentary
Check Point’s VP of Research, Lotem Finkelstein, noted that exploitation of CVE-2026-85102 has expanded globally, with attackers leveraging anonymization infrastructure to evade detection. The company’s advisories stress the importance of reviewing certificate-based login patterns and identifying secondary attack vectors following initial breaches.
Conclusion
The combined vulnerabilities underscore the risks associated with outdated or misconfigured network devices, particularly in environments reliant on cloud-managed solutions. Organizations are urged to prioritize remediation and implement strict access controls to minimize exposure.
About Author

 English