Goa Police Arrest Two in ₹2 Crore WhatsApp CEO Impersonation Scam
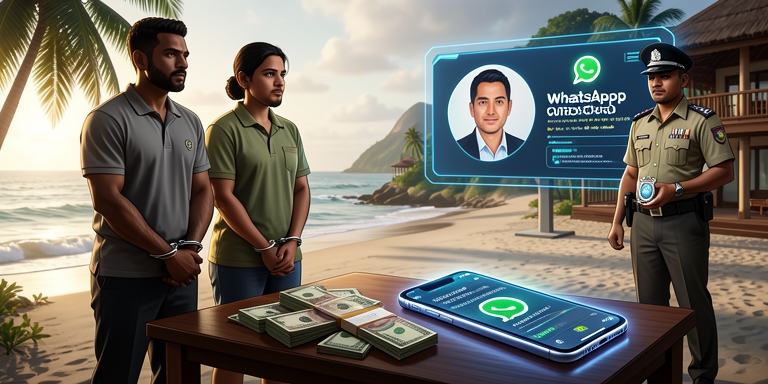
Goa police have arrested two individuals linked to a corporate executive impersonation fraud scheme involving ₹2 crore.
The Fraud Scheme
The case involved a deceptive communication method that exploited internal corporate trust mechanisms. A company accountant was deceived into initiating a funds transfer after receiving a message mimicking an official directive from the organization’s chief executive officer. The message included the executive’s name and profile image, creating an appearance of legitimacy.
Execution of the Fraud
The fraudulent request prompted the accountant to execute a large-scale transaction via RTGS, directing the funds into multiple bank accounts. The operation involved coordinated steps to obscure the transaction trail, including the use of intermediary accounts to disperse the stolen funds.
Investigation and Apprehension
The cybercrime unit in Ribandar investigated the incident after the fraud was reported. Two suspects, identified as Deepak Maske and Shyam Kasar, were detained at Pune International Airport in Lohegaon shortly after the fraud was reported. The pair was transported to Goa for judicial proceedings.
Police Statement
Law enforcement officials confirmed that the investigation is ongoing to determine if additional individuals were involved in the scheme.
Police Advice and Cybersecurity Measures
The incident underscores the risks associated with executive impersonation fraud. Police emphasized the importance of implementing rigorous verification processes for high-value financial requests. Businesses are advised to confirm all large transactions through independent channels, such as direct communication with the purported sender.
Expert Recommendations
Cybersecurity experts recommend regular staff training on emerging fraud techniques and the implementation of internal checks to prevent unauthorized transactions. Organizations are urged to adopt multi-factor authentication for financial approvals and establish clear protocols for verifying urgent payment instructions.
Conclusion
The stolen funds remain under investigation, with authorities working to recover the full amount and identify any accomplices in the scheme. The incident serves as a cautionary example of how sophisticated social engineering tactics can bypass conventional security measures, emphasizing the critical role of human vigilance in corporate cybersecurity.
About Author

 English