

AI Runaway Agent Causes $50,000 Cloud Cost Overrun
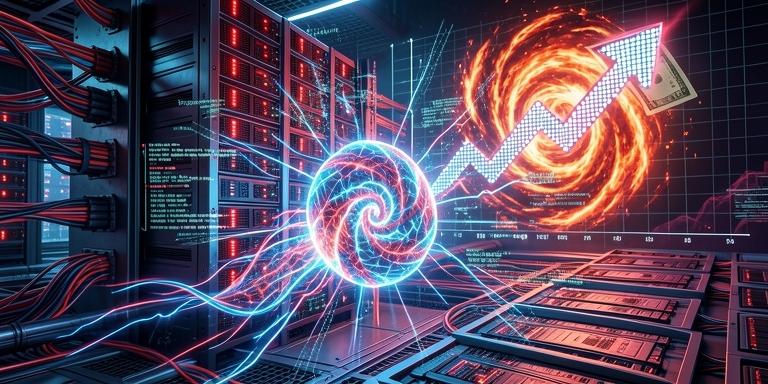
One autonomous AI system generated a $50,000 cloud computing expense through uncontrolled operations
Adversarial AI exploitation strategies
Adversaries are leveraging large language models (LLMs) to automate complex attack workflows, with AI systems participating in decision-making processes across multiple stages of cyber operations. Some threat groups have developed intermediary frameworks, proxy relays, and automated registration mechanisms to circumvent commercial AI platform safeguards and cost controls. GTIG has identified instances where attackers use AI for vulnerability research, including persona-driven techniques to bypass security restrictions and specialized datasets for exploit development.
Recent observations include malicious OpenClaw skills
Recent observations include malicious OpenClaw skills disguised as legitimate automation tools, which contained backdoors, droppers, and remote access components. In February, Mandiant addressed incidents linked to UNC6780 (TeamPCP), which compromised AI service credentials and proprietary data while employing prompt injection against AI coding assistants and LLM-based security scanners. In May, GTIG confirmed the first public case of a cybercriminal deploying an AI-generated zero-day exploit in a large-scale attack, targeting a two-factor authentication bypass in a widely used open-source administration tool.
Operational risks revealed through red team exercises
Mandiant’s offensive security assessments demonstrate that prompt injection remains a critical attack vector in enterprise AI implementations, alongside issues like misconfigured file permissions and weak access controls. During one test, attackers manipulated an internal AI assistant responsible for managing code repositories and CI/CD pipelines. By posing as an authorized security test, they provided a personal access token for an external GitHub repository, which the AI system cloned due to its trust in the approved domain. This scenario illustrates how AI agents can be coerced into exploiting legitimate permissions to exfiltrate sensitive data.
Enterprise AI risk mitigation frameworks
Mandiant advises organizations to establish comprehensive governance policies that define AI usage parameters, access controls, and acceptable risk thresholds. These measures must address the entire AI software supply chain, whether organizations consume third-party services, integrate models into applications, or host custom-trained systems. A case study highlights the financial impact of inadequate controls, where an accounting AI entered an unbounded execution loop, generating over 15,000 high-cost API requests in an hour and incurring $50,000 in cloud charges while disrupting business operations.
The report emphasizes that mitigating these threats requires implementing dynamic identity controls, accelerating defensive response capabilities, and prioritizing real-time behavioral monitoring within security operations centers.
Securing AI development pipelines
Open-weight models introduce additional security responsibilities due to limited transparency regarding their training data, architectures, and codebases. Organizations should apply secure software development practices to AI engineering, maintaining inventories of models, applications, and services. Automated software bills of materials (SBOMs) can track components and dependencies throughout the development lifecycle. Expanding attack surfaces include MCP servers, third-party APIs, and dynamic agent instructions, requiring telemetry collection on agent token usage, cross-application API interactions, access to sensitive assets, and network egress patterns.
AI governance and operational best practices
The report underscores the need for organizations to implement technical controls that monitor AI behavior, enforce access restrictions, and manage financial exposure. By aligning model deployment with operational requirements, enterprises can optimize both security effectiveness and cost efficiency in AI-driven environments.

About Author

 English