

Chinese Hackers Exploit ZyXEL Switch Vulnerability: Cybersecurity Alert
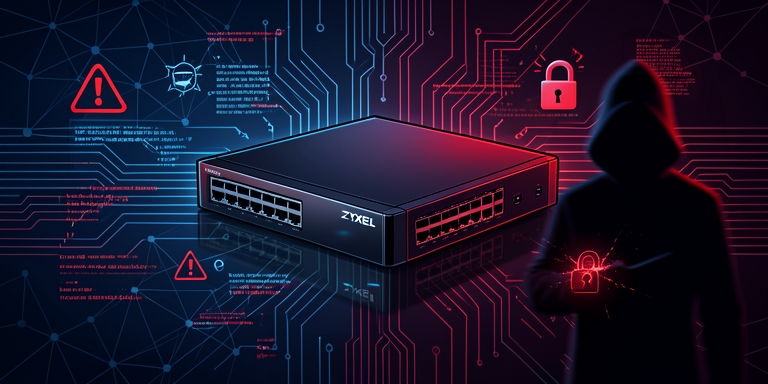
Recent ZyXEL Switch Vulnerability Exploited by Chinese Hackers
Overview of the Vulnerability
According to threat intelligence firm GreyNoise, a Chinese threat actor has been leveraging a critical vulnerability in ZyXEL GS1900 switches to extract sensitive data from devices across 48 countries.
The flaw, designated CVE-2026-7273 with a CVSS score of 8.8, is a stack-based buffer overflow that allows unauthorized execution of operating system commands through specially crafted HTTP requests. ZyXEL addressed the issue in June by releasing patches for ten affected GS1900 switch models.
Details of the Exploit
GreyNoise reported that the exploit was actively used in August by a state-sponsored hacking group targeting firmware versions 2.10 to 2.90 of the GS1900-24 model. The attackers deployed a highly obfuscated Python script to steal hashed root credentials, network configurations, and system details from 996 vulnerable devices.
GreyNoise suggests the group may be connected to the Red Heron hacking collective, which Acronis previously associated with exploiting a Gitea vulnerability in global attacks.
The script includes command-line parameters to adjust for variations in firmware versions, expanding its potential reach beyond the primary target range. The breach revealed that 564 compromised devices were still using factory default login credentials, creating opportunities for further exploitation.
Impact and Scope
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) recently included CVE-2026-7273 in its Known Exploited Vulnerabilities (KEV) catalog, requiring federal agencies to apply patches within three days under BOD 26-04.
GreyNoise reported that the exploit was actively used in August by a state-sponsored hacking group targeting firmware versions 2.10 to 2.90 of the GS1900-24 model.
In addition to the ZyXEL attack, the same threat actor has been linked to a series of campaigns exploiting multiple vulnerabilities. These include a chain of Ubiquiti flaws enabling remote code execution (RCE) and targeted assaults on WordPress installations in July, affecting small businesses and government entities.
Other Campaigns and Attacks
One incident involved the theft of over 18,000 sensitive records from a Western governmental organization’s backend database. The firm also noted the group’s use of advanced techniques to evade detection, including custom scripts and multi-stage exploitation.
Conclusion
The incident underscores the risks of unpatched network infrastructure and the importance of proactive security measures. Organizations are advised to review firmware versions, disable default credentials, and monitor for anomalous traffic patterns. The vulnerability’s exploitation highlights the growing sophistication of state-sponsored actors in targeting enterprise networks through supply chain and device-specific weaknesses.
About Author

 English