

Identity Over Network: Why Identity Security, Not Network Perimeter, Is the New Perimeter
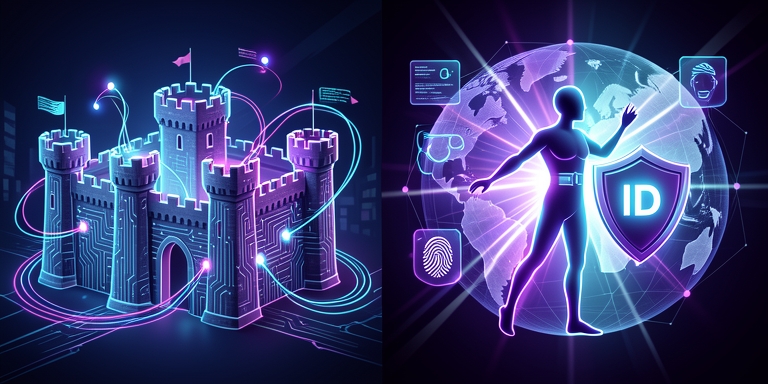
For decades, the Zero Trust model focused on network segmentation, emphasizing advanced firewalls, detailed VLAN configurations, and the principle of “never trust, always verify” as a means of controlling access.
The Evolution of Zero Trust
This approach, however, is encountering significant limitations in modern cloud-native environments, particularly those leveraging Kubernetes and multi-cloud infrastructures. Many teams have yet to fully address the fundamental challenge: the instability of network perimeters in dynamic cloud environments.
In Kubernetes clusters, the network infrastructure is inherently transient. Workloads scale rapidly, with pods frequently launching and terminating within seconds. IP addresses are ephemeral, constantly reassigned as resources shift. A workload that existed moments ago may no longer be present, replaced by another entity with a distinct identity, even if it performs the same function.
Traditional Zero Trust frameworks that rely on network location and IP-based trust mechanisms are ill-suited to secure an environment where the perimeter is in constant flux. Organizations that have adapted to this reality have shifted their focus from querying “what network segment is this traffic originating from” to asking “what is this workload, and can it cryptographically verify its identity?”
The Three Pillars of Modern Zero Trust
This represents a fundamental architectural shift rather than a simple policy adjustment. The foundation of this approach rests on three pillars: identity-centric microsegmentation, workload attestation, and continuous risk assessment across multi-cloud environments.
Identity-Centric Microsegmentation
Microsegmentation must align with workload identity rather than network subnets. Traditional microsegmentation defines boundaries around static network zones, but cloud-native environments require boundaries to follow workloads. Every service-to-service interaction is evaluated based on the cryptographic identity of the requesting workload, not the subnet it occupies at a given moment.
This approach mitigates risks associated with static Kubernetes service account tokens or outdated IP-based allow rules, which can persist long after the underlying workload has changed.
Workload Attestation
Workload attestation addresses the “secret zero” vulnerability. Standards like SPIFFE and SPIRE have become essential for establishing trust in cloud-native settings. NIST SP 800-207A explicitly recognizes SPIFFE as application identity infrastructure for Zero Trust in multi-cloud environments.
The core concept involves issuing short-lived cryptographic identities through a chain of attestation rather than distributing static secrets. A node verifies its identity using platform evidence, such as cloud instance metadata or TPM measurements, while a workload demonstrates its identity via process-level data like namespace, service account, or container image digest.
Only after both validations succeed does the workload receive a SPIFFE identity document, typically valid for approximately one hour before automatic rotation. This ensures that stolen credentials become obsolete within an hour, contrasting with the long-term validity of leaked API keys.
Continuous Risk Assessment
Continuous risk assessment remains the most challenging component for many organizations. While identity and attestation handle authentication, they do not address governance across complex multi-cloud estates.
Traditional approaches often rely on periodic scans, such as quarterly cloud security posture reviews, which fail to reflect real-time conditions. In environments where identities and infrastructure change hourly, a risk posture assessed quarterly becomes outdated by the time it is reviewed.
True continuous risk assessment requires treating posture data as dynamic, integrating real-time monitoring and adaptive controls.
The Path Forward
Implementing these changes does not necessitate discarding existing infrastructure. SPIFFE and SPIRE are already proven at scale, and Kubernetes-native tools can integrate cryptographic identity directly into network policy enforcement without altering application code or migrating to a full service mesh.
The primary challenge lies in organizational alignment, ensuring security, platform engineering, and cloud governance teams prioritize identity as the central control plane.

About Author

 English