

Essential Guide to Digital Evidence for Law Enforcement Professionals
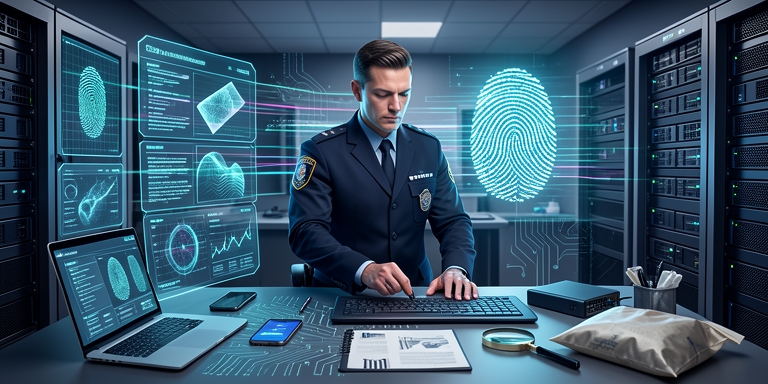
Digital evidence has become a critical component of modern criminal investigations, extending beyond cybercrime to encompass a wide range of offenses including murder, financial fraud, and organized crime.
Understanding the Concept of Digital Evidence
Digital evidence refers to any information stored or transmitted in digital form that holds relevance to an investigation or legal case. This includes data from computers, mobile devices, cloud platforms, surveillance systems, and communication networks. Investigators must determine the origin, integrity, and authenticity of such evidence, as its reliability is crucial for legal admissibility. Unlike physical evidence, digital data can be altered, deleted, or overwritten, necessitating strict preservation protocols.
The Digital Evidence Investigation Process
A structured approach is essential for effective digital evidence collection and analysis. The process typically involves the following stages:
- Identification: Locating relevant electronic sources such as devices, accounts, or network records.
- Preservation: Protecting evidence from accidental modification or loss.
- Collection: Acquiring data through legally sanctioned methods, such as forensic imaging or data extraction.
- Examination: Analyzing recovered files, metadata, and system logs to identify patterns or connections.
- Documentation: Recording all steps to ensure transparency and traceability.
Each phase requires meticulous attention to detail, as gaps in documentation can undermine the credibility of findings.
Key Categories of Digital Evidence in Investigations
Digital evidence spans multiple domains, each requiring specialized techniques:
- Smartphones: Contain messages, call logs, location data, and app activity.
- Computers: Store documents, browsing history, and system logs.
- Networks: Generate logs of traffic, authentication attempts, and device connections.
- Cloud Platforms: Host backups, synchronized files, and account records.
- CCTV Systems: Provide video footage and metadata for event reconstruction.
- Financial Records: Include transaction logs, cryptocurrency activity, and banking data.
- Social Media: Offer insights into communications, uploaded content, and user behavior.
Each category demands tailored preservation and analysis strategies to maintain evidentiary integrity.
Technologies and Tools for Digital Evidence Examination
Forensic investigations rely on advanced technologies to extract and analyze digital data:
- Forensic Imaging: Creates exact copies of storage media for examination without altering the original.
- Mobile Forensics: Tools like Cellebrite enable data recovery from smartphones, though encryption and security measures can limit access.
- Computer Forensics: Software such as EnCase and FTK processes file systems, deleted data, and user activity.
- Network Forensics: Tools like Wireshark capture and analyze network traffic for patterns or anomalies.
- Cloud Forensics: Requires cooperation with service providers and legal authorization to access remote data.
- Multimedia Analysis: Techniques verify the authenticity of images, videos, and audio files, addressing challenges like deepfakes.
- Hashing: Cryptographic functions like SHA-256 validate data integrity by comparing hash values before and after acquisition.
These tools are indispensable but require trained personnel to interpret results accurately.
The Importance of Preservation and Chain of Custody
Preservation is the cornerstone of digital evidence handling. Electronic data can be lost through accidental deletion, system updates, or remote wiping. Investigators must use write-blocking devices and controlled environments to prevent tampering. The chain of custody—a documented record of evidence handling—ensures accountability and transparency. Key elements include:
- Device identification and acquisition method.
- Timestamps and locations of collection.
- Names of personnel involved.
- Hash values for integrity verification.
A robust chain of custody is vital for proving that evidence has not been compromised.
Recovering Deleted Digital Evidence
While deletion does not always erase data permanently, recovery is not guaranteed. Factors such as encryption, secure deletion protocols, and storage optimization can render data inaccessible. For example, modern smartphones often employ hardware-backed encryption, complicating forensic access. Even recovered data requires contextual analysis to establish its relevance and origin.
Digital Evidence in Cybercrime Investigations
Digital evidence is pivotal in addressing cyber threats like phishing, ransomware, and financial fraud. For instance:
- Phishing Investigations: Analyze email headers, domain registration details, and account activity.
- Ransomware Cases: Examine malware samples, system logs, and attacker communication channels.
- Financial Fraud: Trace transaction records, device fingerprints, and communication metadata.
Correlating data from multiple sources helps establish timelines and relationships, though investigators must avoid assuming direct links between digital identifiers (e.g., IP addresses) and individuals.
Challenges with CCTV and Multimedia Evidence
CCTV footage and multimedia files present unique challenges. Timestamp discrepancies, metadata alterations, and compression artifacts can affect reliability. Deepfake technology further complicates verification, as synthetic media can mimic real content. Forensic experts use specialized tools to detect manipulations, but conclusive results often depend on original files and system logs.
Legal Framework for Digital Evidence in India
India’s legal system recognizes digital records as admissible evidence under the Bharatiya Sakshya Adhiniyam, 2023, and the Bharatiya Nagarik Suraksha Sanhita, 2023. Key provisions include:
- Section 61: Outlines the legal effect of electronic records, subject to verification under Section 63.
- Section 193(3)(i): Mandates documentation of electronic device custody in police reports.
Investigators must adhere to these frameworks to ensure evidence meets legal standards, as technical recovery alone does not guarantee admissibility.
Current Use of Digital Forensics by Law Enforcement
Digital forensics is a well-established practice in law enforcement. In India, the Indian Cyber Crime Coordination Centre supports national cybercrime investigations through training and coordination. Internationally, Europol and INTERPOL provide technical and analytical support for cross-border cybercrime cases. While these agencies leverage advanced tools, they are not fully AI-driven systems, highlighting the distinction between existing capabilities and emerging technologies.
The Role of Artificial Intelligence in Digital Evidence
AI enhances digital evidence analysis by automating tasks such as document classification, image recognition, and pattern detection. However, its use introduces risks, including misinterpretation of data or reliance on flawed algorithms. Investigators must validate AI-generated findings through manual verification and document analytical processes. AI serves as a tool to augment, not replace, human expertise.
Common Mistakes by First Responders
First responders must avoid actions that compromise evidence integrity:
- Operating seized devices before documenting their state.
- Copying data without verifying its source or integrity.

About Author

 English