

5 Legitimate ‘No Change’ Decisions: No-Action, Monitor, Defer, Transfer, Risk Acceptance
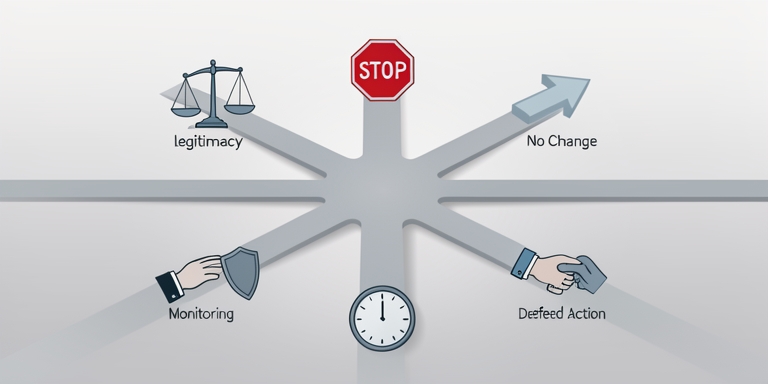
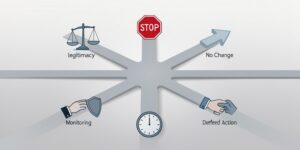
The five legitimate ‘no change’ decisions: no-action, monitor, defer, transfer, and risk acceptance
Introduction
The instinct to address every alert, recommendation, or audit flag as an urgent remediation task creates operational inefficiencies. When identity and access management teams treat all findings as mandatory fixes, it leads to excessive ticket queues, obscured critical risks, and misplaced priorities. Non-remediation choices are valid risk management strategies rather than oversight gaps.
Decision Types
Decision 1: No action — confirmed existing coverage
This choice applies when an established control already addresses the risk, supported by verifiable evidence. Unlike negligence, a valid no-action decision requires documentation specifying the control, its verification date, and the responsible party. A failure occurs when an analyst closes a ticket citing “covered by MFA policy” without confirming the policy’s scope, such as overlooking service-account exemptions.
Decision 2: Monitor
This option applies when the current risk does not necessitate immediate change but could evolve. Monitoring involves active oversight with a designated owner, defined thresholds, and automated escalation mechanisms. A legitimate monitor decision includes a review schedule and clear criteria for triggering alerts. A failure occurs when monitoring is logged without follow-up, leading to unaddressed risks in environments with high service-account activity.
Decision 3: Defer
This choice applies when remediation is necessary but delayed due to operational constraints, such as pending migrations or scheduled maintenance windows. Unlike monitoring, defer explicitly acknowledges future action with a set deadline. A failure occurs when the decision lacks a specific date or owner, allowing delays to become permanent.
Decision 4: Transfer
This involves shifting responsibility for a risk to another team, system, or third party that manages the affected asset. The transferring team must confirm the recipient’s ability to address the issue. In complex enterprises, transfer decisions often fail due to unclear ownership of assets, such as orphaned service accounts or untracked API tokens.
Decision 5: Risk acceptance
This applies when an organization determines that the cost of remediation outweighs the potential impact of the risk. NIST SP 800-39 emphasizes that risk acceptance requires explicit organizational approval from an accountable authority, not just analyst discretion. A failure occurs when high-volume findings are bulk-accepted without proper evidence, such as risk descriptions, affected systems, and approver details.
According to NIST SP 800-39, risk response involves deliberate options such as acceptance, avoidance, mitigation, transfer, and monitoring. A documented decision not to alter a control represents a recognized risk outcome, not an omission.
All five decision types become problematic without clear rationales, named responsible parties, or processes for revisiting choices. In regulated environments, undocumented risk acceptance or no-action decisions may be flagged as control gaps by auditors.
NIST SP 800-39: https://csrc.nist.gov/pubs/sp/800/39/final
This content was reviewed and approved by a cybersecurity practitioner participating in CyberRisk Alliance’s Expert Review Program. Reviewers assess technical accuracy, relevance, and alignment with current industry practices.

About Author

 English