

Patching and Preventing Issues: Essential Strategies and Lessons Learned
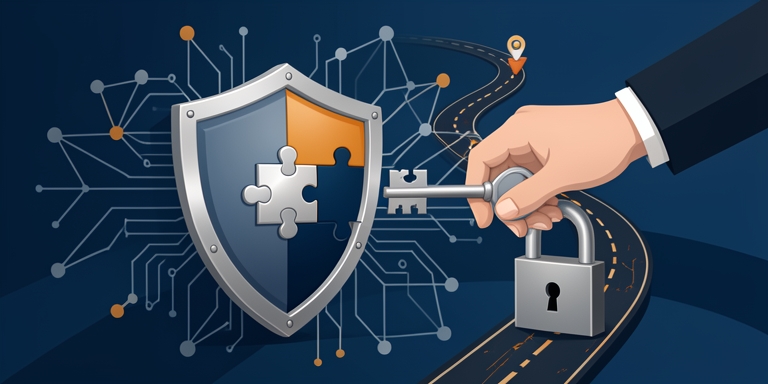
Patching and proactive security strategies remain critical challenges for organizations despite years of investment in tools and processes.
Systemic Obstacles in Effective Remediation
Kunal Modasiya, Senior VP GM at Qualys, highlights systemic obstacles that hinder effective remediation efforts. He emphasizes that patching involves more than addressing individual vulnerabilities, as complex dependencies and configuration changes often complicate full resolution.
Business Constraints and Operational Priorities
Business constraints further delay implementation, with mission-critical systems prioritizing operational continuity over immediate security fixes. Unintended consequences from patch deployments, such as system downtime, also create hesitation among IT teams.
The Role of Executive Support
Executive support is essential to justify the financial and operational risks associated with updates, requiring security leaders to frame remediation in business terms rather than purely technical ones.
Automation and AI-Driven Solutions
The industry’s focus on speed has reached limitations, as manual workflows and human intervention slow large-scale patching. While automation improves efficiency, AI-driven tools can enhance testing and decision-making by analyzing risk profiles and deployment scenarios.
Proactive Threat Prioritization
Proactive teams prioritize business-specific threats over standardized metrics like CVSS scores, integrating threat intelligence, asset inventory, and operational impact assessments. This approach enables faster responses to emerging risks, such as vulnerabilities that evolve into attack vectors.
Revising Metrics for Better Outcomes
Modasiya advocates for shifting from traditional metrics like Mean Time To Remediation (MTTR) to evaluating Remediation Efficiency, which considers the window of exposure (AWE) and the speed at which attackers weaponize vulnerabilities (WOW). The gap between these metrics reveals critical exposure periods where adversaries hold the advantage.
Automated vs. Human-Driven Patching
Automated patching is viable for low-risk systems with minimal business impact, such as non-critical applications, but high-risk environments require human oversight. Future advancements in agentic AI could revolutionize remediation by prioritizing vulnerabilities based on real-world context, rather than generic classifications.
For example, Microsoft’s monthly Patch Tuesday updates may not align with an organization’s unique risk profile, necessitating tailored recommendations. AI-driven systems can identify priority issues, streamline ownership assignments across departments, and accelerate remediation workflows.
Addressing Ownership and Strategic Decision-Making
Organizations must also address ownership challenges, ensuring accountability for patching across business units. While automated solutions reduce manual effort, strategic decision-making remains vital for critical systems. As threat landscapes evolve, integrating AI into security operations will enhance agility, enabling faster risk mitigation and reducing exposure to emerging threats.
Critical Vulnerabilities and Urgency
Critical vulnerabilities like CVE-2026-97229 underscore the urgency of proactive measures, as unpatched systems remain targets for exploitation. The shift toward AI-assisted remediation reflects a broader trend in cybersecurity, where data-driven insights and automation play pivotal roles in safeguarding enterprise environments.
About Author

 English