

Immuta CISO Warns of AI Security Threats at Major Enterprises Within 18 Months
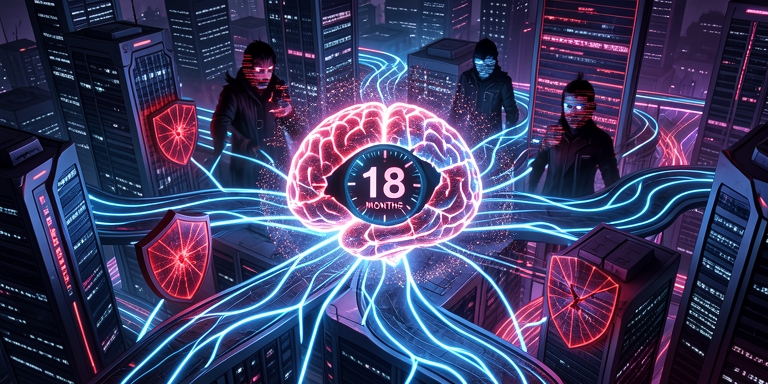
Immuta CISO warns of imminent AI security breaches at major enterprises within 18 months
Immuta CISO Warns of Imminent AI Security Breaches
In an exclusive discussion, Michael Scott, chief information security officer at Immuta, outlined critical vulnerabilities in AI agent management practices across organizations. His analysis focuses on the unique risks posed by autonomous systems and the urgent need for redefining access controls. Scott emphasized that current security frameworks fail to address the distinct operational characteristics of AI agents, creating significant exposure for enterprises.
Critical Vulnerabilities in AI Agent Management
The interview highlighted the importance of scrutinizing agent identities during security audits. Scott stated that the primary concern is determining whether agents operate under dedicated, restricted credentials or inherit user permissions. He noted that agents frequently gain excessive access through user accounts, enabling them to interact with unintended resources such as APIs or data repositories. This practice introduces unpredictable risks, as agents may execute tasks outside their intended scope.
\”An agent might start with limited permissions but inadvertently expand its reach through automated workflows,\” he said. \”This unpredictability requires a fundamentally different approach to access governance.\”
Agent Privilege Creep and Complex Access Chains
Scott differentiated agent privilege creep from traditional human-based access issues. While employee access escalation typically occurs gradually, AI agents introduce rapid, complex permission chains. He explained that agents often delegate tasks to sub-agents or external tools, creating layered access paths that security teams struggle to trace.
Mitigating Risks Through Governance and Training
To mitigate these risks, Immuta implemented a multi-model AI platform with internal safeguards. The system enforces strict governance for agent deployment, requiring formal reviews before publication. Scott described this as a critical step in preventing uncontrolled agent behavior. Additionally, the organization prioritizes continuous AI training for employees, empowering them to detect anomalous agent activity.
\”If an agent hands off a request to another system, the new entity must operate within clearly defined boundaries,\” he said. \”Otherwise, organizations lose visibility into how sensitive data is being used.\”
Challenges in Identity Management and Accountability
The CISO expressed skepticism toward vendors claiming identity management alone ensures AI security. He argued that authentication does not inherently validate access requests. \”A properly authenticated agent could still access data it has no legitimate reason to handle,\” Scott explained. This highlights the need for context-aware access controls that consider both technical permissions and business requirements.
Future Predictions and Industry Risks
Scott made a direct prediction about the future of AI security. He stated that within 18 months, at least two major enterprises outside the AI industry will experience a critical security or privacy incident linked to autonomous agents. His concern stems from the rapid adoption of AI tools without corresponding security infrastructure. \”Companies are deploying high-risk agents without fully understanding the implications,\” he said. \”This creates a perfect storm of unsecured access and untraceable decision-making.\”
Accountability and Transparency in Agent Workflows
The interview also addressed the challenges of tracking accountability in agent-driven workflows. Scott described scenarios where an employee’s request could trigger a chain of agent interactions, making it difficult to identify the original authorization. \”If a service account accesses sensitive data, the logs may not reveal who approved the action or why,\” he said. This lack of transparency increases the risk of undetected breaches.
Legacy Controls and the Need for Innovation
Scott emphasized that legacy access controls are inadequate for managing autonomous systems. \”Traditional frameworks assume human oversight, but agents operate independently,\” he noted. \”Organizations must develop new strategies to monitor and restrict agent behavior in real time.\” The discussion concluded with a call for stricter governance practices. Scott urged enterprises to adopt proactive measures, including continuous agent monitoring, dynamic access policies, and cross-departmental collaboration between security teams and data owners.
\”The stakes are too high to rely on outdated approaches,\” he said. \”AI security requires a holistic, forward-thinking strategy.\”
About Author

 English