

Automation vs AI vs Humans: How to Handle Security Findings
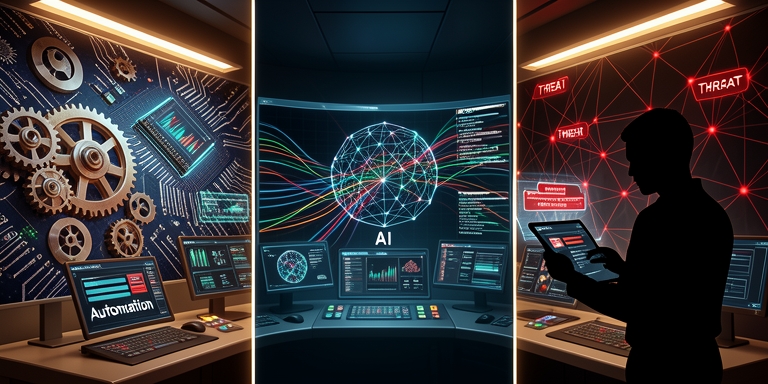
Over half of the 200 senior security and technology leaders surveyed by ArmorCode indicated their organizations face challenges in simplifying software security programs if current practices continue. The respondents, primarily from companies with 10,000 or more employees, highlighted difficulties in managing vulnerabilities once detected by scanning tools. The process involves assessing the significance of flaws, identifying ownership, and coordinating fixes across teams using disparate tools and release cycles. Delays in this chain increase exposure to known vulnerabilities, with
The rise of AI tools has intensified pressure on security teams. Developers use AI to accelerate software creation, while AI-assisted scanning identifies more weaknesses. Forty percent of survey participants cited the volume of AI-generated code requiring human review as a major challenge. While AI code is not inherently insecure, the sheer volume exceeds human capacity for thorough evaluation. This figure reflects individual responses to a limited-choice question, offering no insight into how the remaining 60% perceive the issue.
Tiered Approach to Vulnerability Management
A tiered approach to vulnerability management emerged as the top priority for 44% of respondents. Automation should handle repetitive tasks such as deterministic findings, remediations, and mitigations that follow established protocols. Most organizations already implement some level of automation for these activities, integrating them into workflows like normalization, enrichment, ownership assignment, ticket management, and rescan verification.
AI agents are positioned for tasks requiring multi-step reasoning with minimal oversight
These systems can evaluate exploitability, identify correlated vulnerabilities, and map potential attack paths. However, their use demands robust audit trails and review mechanisms due to the judgment required. Human involvement remains critical for decisions involving risk acceptance and exceptions, ensuring accountability. The ideal model involves a layered strategy where findings escalated to humans are analyzed for opportunities to delegate similar tasks back to automation.
Low-Context Alerts
Low-context alerts pose another significant concern. Security leaders cited these as their primary worry, as they often lack essential details such as system accessibility, exploitability, business impact, or ownership. Teams overwhelmed by such alerts face both volume and context challenges.
Coordination Across Tools
Coordination across tools and workflows further complicates remediation. A single vulnerability may traverse multiple systems, requiring input from security teams, developers, and external vendors. Consolidating overlapping tools while retaining those offering unique coverage is recommended. Security leaders should evaluate tools based on coverage, signal quality, integration capabilities, and user trust.
Key Metrics for Boardroom Reporting
About Author

 English