

Elementor WordPress Security Flaw: One Click Grants Admin Access
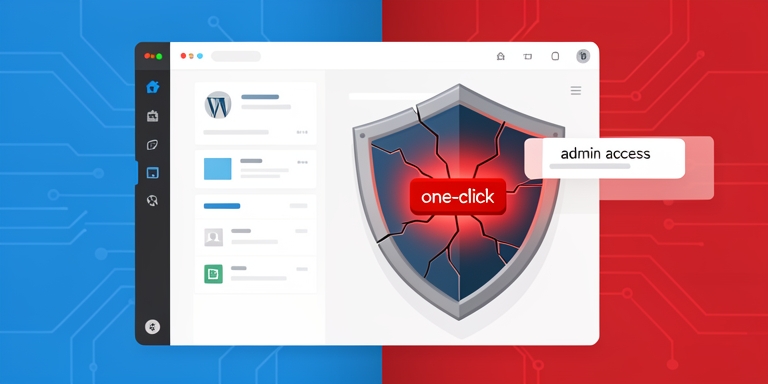
A critical security flaw in the Elementor Website Builder plugin for WordPress has been identified, enabling attackers to gain administrative control through a single user interaction.
Affected Elementor Versions and Their Impact
The flaw is present in Elementor Website Builder versions 4.3.0 and 4.3.1, which are deployed on approximately 2 million websites globally. These versions are part of a widely used tool that simplifies website creation through a visual drag-and-drop interface. The vulnerability remains unassigned a formal identifier, but its implications are significant due to the plugin’s prevalence.
Mechanism of the Vulnerability
Security researchers at Patchstack discovered that the flaw arises from the plugin’s handling of REST API requests. Attackers can craft a malicious link that leverages the plugin’s URI structure to execute unintended actions. When a logged-in administrator accesses this link, the system processes the request using their existing privileges. This allows the attacker to trigger actions permitted by the administrator’s account, such as modifying site settings or creating new user roles.
Exploitation Without Additional Code
Unlike many cyberattacks, this vulnerability does not require JavaScript, phishing pages, or form submissions. The exploit relies solely on a crafted URL that an attacker can deliver via email, messaging platforms, or embedded in website comments. Once the target opens the link, the system executes the malicious request under their administrative credentials.
Potential for Privilege Escalation
The flaw enables attackers to create a new administrator account controlled by the malicious actor. This is achieved by exploiting the REST API to perform actions that the compromised account is authorized to execute.
Mitigation and Recommendations
Users of the affected versions are strongly advised to update to Elementor 4.3.2 immediately. Staying on 4.3.0 or 4.3.1 leaves systems exposed to potential exploitation. Additionally, reverting to earlier versions is not recommended, as some older releases contain actively exploited vulnerabilities.
Key Takeaway
This incident underscores the risks associated with privileged user interactions and the importance of timely software updates. Administrators must verify their installed Elementor versions and apply patches promptly to prevent unauthorized access. The vulnerability highlights how seemingly minor flaws in widely used tools can have broad security implications.
About Author

 English