

Rajasthan Police Arrest 12th Accused in 6.80 Crore Cyber Fraud Case
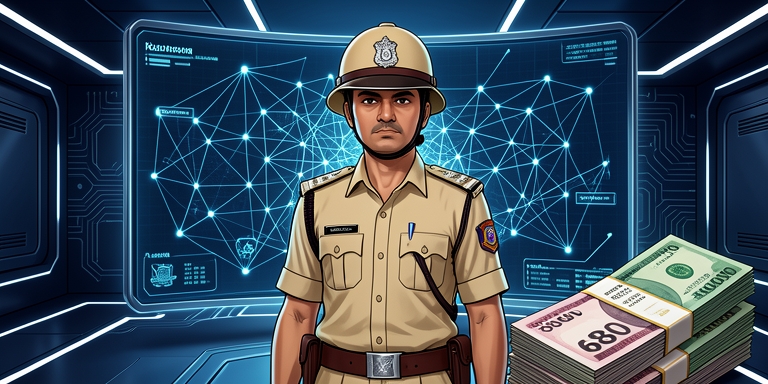
Rajasthan Police have detained a Bikaner-based individual linked to a cyber fraud scheme involving 680 million rupees, marking the twelfth arrest in an ongoing probe.
Arrest and Investigation Details
The suspect, Laxman Singh known as Neeshu, is accused of facilitating a cybercriminal network by acquiring bank accounts, personal identification documents, active mobile SIM cards, and hotel accommodations. The scheme targeted a private organization, where attackers infiltrated internal systems to impersonate a corporate executive and redirect funds into unauthorized accounts. Investigators confirmed that Singh maintained communication with key members of the fraud syndicate via a Telegram group named F2F Jaipur Delhi.
Suspect’s Role
The suspect, Laxman Singh known as Neeshu, is accused of facilitating a cybercriminal network by acquiring bank accounts, personal identification documents, active mobile SIM cards, and hotel accommodations.
Scheme Details
The scheme targeted a private organization, where attackers infiltrated internal systems to impersonate a corporate executive and redirect funds into unauthorized accounts.
Communication and Evidence
According to officials from the state’s Cyber Crime Directorate, Singh arranged lodging for an associate, Sandeep Kumar, at a Reengus hotel on August 23. During this encounter, Singh allegedly obtained banking materials including passbook kits, chequebooks, ATM cards, and a mobile SIM card linked to the fraudulent operation. The acquired financial instruments were critical to the syndicate’s activities. Police reported that the recovered SIM card was immediately deployed to execute fraudulent transactions.
Financial Trail and Methods
The scheme began after a company employee was misled by impersonators posing as a director, leading to the transfer of 680 million rupees across three bank accounts on August 24. The deception was uncovered when internal audits revealed the director had not authorized the transfers. The perpetrators employed multiple layers of obfuscation to conceal the financial trail, utilizing mule accounts, ATMs, Unified Payments Interface (UPI) channels, QR codes, cheques, cash deposit machines, and conversions into digital assets such as USDT cryptocurrency.
Ongoing Investigation
Authorities have expanded their investigation to dismantle the support infrastructure sustaining such cybercrime operations. Specialized units are analyzing communication records, banking transactions, and hotel guest logs to identify secondary networks providing financial tools to syndicates. State cybercrime officials confirmed the inquiry remains active, with efforts focused on locating additional accomplices managing Telegram-based transaction channels and tracing the final destinations of cryptocurrency assets.
About Author

 English