

Scam Alert: Fake Claude Max Giveaway Tricks Users into Sharing Google Credentials
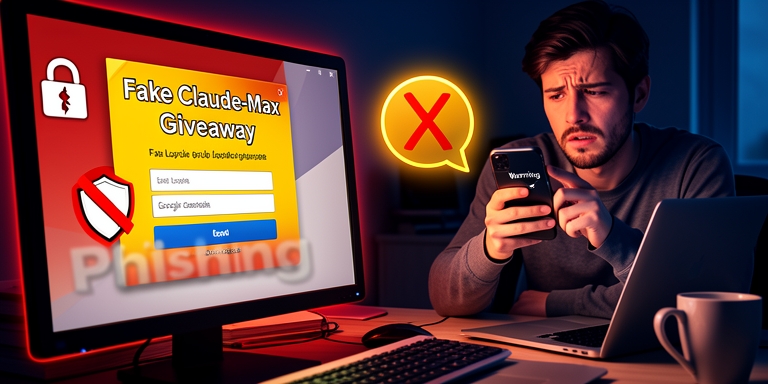
Malwarebytes researchers uncover a phishing campaign using a spoofed Google sign-in interface to steal credentials for free Claude Max access.
Phishing Campaign Details
A phishing campaign exploiting a spoofed Google sign-in interface has been identified by Malwarebytes researchers, targeting users with a fraudulent offer for free access to the Claude Max subscription service. The attack leverages a browser-in-the-browser technique, a method documented since 2022, to deceive victims into revealing their credentials.
Browser-in-the-Browser Technique
Researchers noted that phishing tactics adapt to user interests, with this campaign capitalizing on the popularity of AI chatbots. Claude’s paid plans range from $20 monthly for basic access to higher-tier pricing, making the promise of a free upgrade a compelling lure.
Microsoft Report on Similar Campaigns
Microsoft’s June report highlighted similar campaigns impersonating ChatGPT, Claude, DeepSeek, and Copilot, often involving fake payment alerts or checkout pages. This particular scheme differs by omitting card detail requests and instead using urgency-driven tactics.
Fake Website Features
The malicious website replicates Claude’s branding, including its logo and color scheme, and claims the service has surpassed 100 million users. It promotes a giveaway of 10,000 free one-month Max subscriptions, featuring a countdown timer that updates every few seconds to create scarcity.
Scam Credibility Enhancements
The displayed number of remaining slots is generated client-side and resets upon page reload. A FAQ section explicitly states no payment information is required, a detail that enhances the scam’s credibility.
Sign-In Interface Deception
Users are directed to a sign-in interface with multiple options, but only the Google button functions. Clicking this button triggers a simulated browser window within the same tab, complete with a padlock icon and a legitimate-looking Google URL. This window can be moved across the screen and includes a human verification step instead of a password field, potentially evading automated detection tools.
Malicious Code Analysis
The malicious code relies on a single line of external script, presented as a reusable sign-in widget. Russian-language comments in the code reference the target as “the victim” and describe adjustments to the window’s appearance to avoid detection.
Consequences and Expert Advice
Researchers concluded the code represents a modular, reusable tool rather than a one-off campaign. Compromised Google accounts grant attackers access to emails, documents, and password reset capabilities for other services, while also enabling unauthorized access to Claude. The attack highlights evolving phishing strategies that combine social engineering with technical sophistication to bypass traditional security measures.
Security Recommendations
Security experts advise users to verify unexpected offers through official channels and maintain vigilance against unsolicited requests for authentication details.
“This particular scheme differs by omitting card detail requests and instead using urgency-driven tactics.” – Malwarebytes Researchers
“Researchers concluded the code represents a modular, reusable tool rather than a one-off campaign.” – Malwarebytes Researchers
About Author

 English