

Security Breach: Thousands of Zyxel Switches Compromised Since August (CVE-2026-7273)
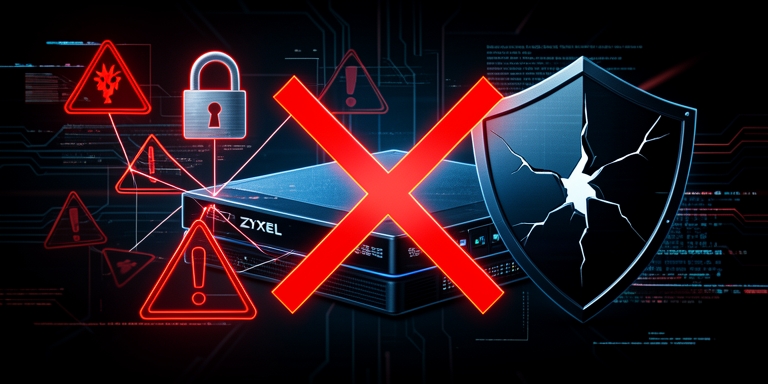
Attackers exploited a critical vulnerability in Zyxel switches, compromising 996 devices across 48 countries.
Attack Overview
A threat group associated with a Chinese-speaking actor has leveraged a security flaw (CVE-2026-7273) in unpatched ZyXEL GS1900 Smart Managed Switches to gain access to 996 devices across 48 nations, according to GreyNoise analysis published on Monday.
According to GreyNoise analysis published on Monday.
Affected Devices and Regions
The affected hardware is primarily concentrated in Italy, the United States, Taiwan, South Korea, and multiple European Union member states.
Vulnerability Details
The vulnerability, a stack-based buffer overflow, impacts firmware versions 2.90(XXXX.1)C0 and earlier. It enables a local area network-based attacker to execute arbitrary operating system commands through a specially crafted HTTP request without authentication.
Exploitation Timeline
GreyNoise identified exploitation attempts occurring on or around August 17, during which the threat actor extracted device configurations, network data, and hashed root credentials from compromised systems.
Threat Actor’s History
The malicious code employed in the attack was embedded within a Python script that utilized the PyArmor obfuscation tool to conceal its functionality. GreyNoise linked this activity to a threat actor previously linked to campaigns targeting WordPress platforms via CVE-2026-63030 and CVE-2026-60137 (the WP2Shell exploit chain), as well as attacks on Internet-facing Gitea instances using CVE-2026-60004.
CISA’s Response
The Cybersecurity and Infrastructure Security Agency (CISA) has included CVE-2026-7273 in its Known Exploited Vulnerabilities catalog, mandating U.S. civilian federal agencies to address the issue by September 24, 2026, and conduct forensic analysis for signs of intrusion.
Arctic Wolf’s Report
Concurrently, Arctic Wolf reported ongoing exploitation of CVE-2026-32996, a local privilege escalation vulnerability in the Veeam Agent for Microsoft Windows. Users are advised to update to Veeam Backup Replication version 13.0.2.29 or later, which also updates the Veeam Agent for Windows to build 13.0.3.1220, incorporating the fix.
About Author

 English