

Singapore’s New Cybersecurity Strategy: Revamping Against AI-Driven Threats
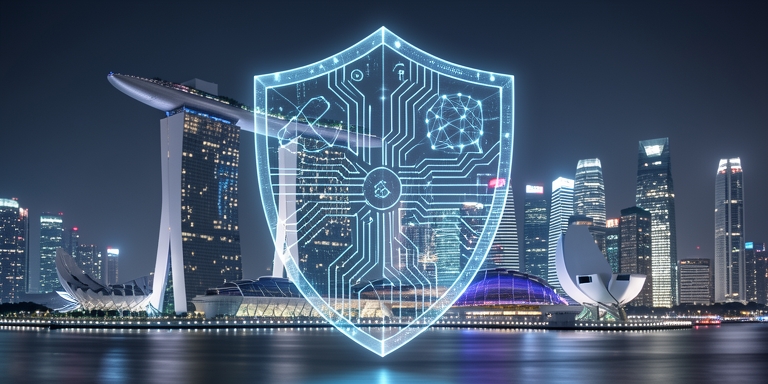
Singapore has revised its cybersecurity framework in response to incidents attributed to UNC3886, integrating artificial intelligence into government operations and enhancing capabilities to identify malicious actors within critical networks.
Revised Cybersecurity Framework
The updated approach prioritizes proactive detection and mitigation of threats rather than solely focusing on perimeter defenses. The shift stems from a recent cyberattack targeting four major telecommunications providers, which exposed vulnerabilities in existing security protocols.
Proactive Threat Detection
Officials emphasized that advanced persistent threat groups can infiltrate systems and remain undetected for extended periods. This necessitates a strategy that assumes potential breaches and focuses on rapid identification and containment of intrusions.
Artificial Intelligence in Defense
Artificial intelligence plays a central role in the new defense model. Government agencies have deployed AI-driven tools to conduct automated vulnerability assessments across 2,000 systems, including those handling sensitive citizen data. These tools simulate cyberattacks to uncover exploitable weaknesses.
Code Analysis and Insider Threats
A second AI application analyzes source code for security flaws, enabling agencies to address vulnerabilities before adversaries exploit them. Efforts to detect insider threats involve enhanced monitoring of internal network activity. Authorities are implementing continuous traffic analysis to identify anomalous behavior.
Critical Infrastructure Security
Critical infrastructure sectors, including energy, healthcare, and finance, are set to benefit from expanded AI security measures. The Cyber Security Agency of Singapore is evaluating the integration of these tools into 11 key industries, assessing operational requirements and sector-specific risks.
External Scans and Threat Intelligence
Regular external scans of internet-facing systems are being conducted to identify unpatched software and misconfigured assets. Supplementary defenses include the deployment of proprietary threat-detection systems developed by a Ministry of Defence-affiliated technical agency. Classified threat intelligence is being shared with critical infrastructure operators.
Supply Chain and Strategic Priority
Supply chain risks are under review, with potential requirements for vendors to obtain Cyber Essentials or Cyber Trust certifications by 2027. Cybersecurity is now framed as a strategic priority, reflecting its impact on national security, economic stability, and public confidence.
Global Context and Resilience
The evolution mirrors global tensions over access to advanced technologies and the increasing reliance on digital systems. Disruptions to these networks could affect essential services, prompting a transition toward a proactive, resilience-focused model.
Conclusion
Singapore’s strategy underscores a paradigm shift in cybersecurity. Traditional perimeter defenses are no longer sufficient against evolving threats. Organizations must adopt continuous surveillance, proactive threat identification, and anomaly detection to counter sophisticated adversaries and AI-driven attacks.
About Author

 English