

ASOS Data Breach Confirmed: Hacked App Alert Sparks Customer Concerns
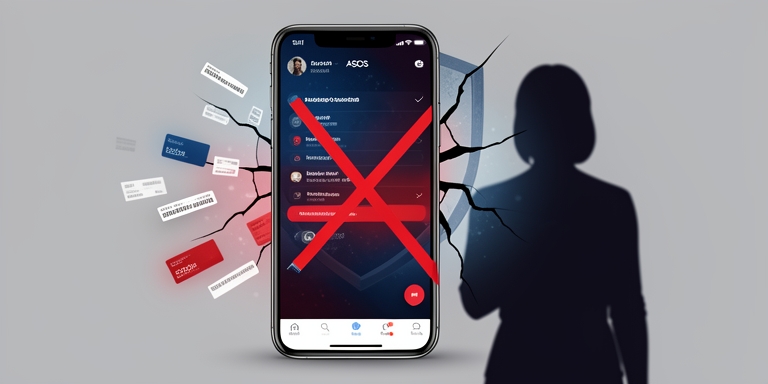
ASOS confirms data breach after “hacked” app alert reaches shoppers
Cybersecurity incident involving ASOS
A cybersecurity incident involving the UK-based fashion retailer ASOS has been disclosed following an unauthorized notification sent to customers via its mobile application. The breach was first detected when users received a message alleging that hackers had infiltrated the company’s systems. The notification, which appeared through the app, prompted immediate investigation by the organization. The company, which was established in 2000 and operates in over 100 markets, reported that the unauthorized communication was distributed around 10:00 AM on October 6, 2026.
Third-party platforms involved
In a statement released to investors, ASOS indicated that the breach involved third-party platforms used for customer communication. The retailer confirmed it had taken steps to limit access to these platforms and was collaborating with internal and external security experts as well as regulatory authorities.
Potential data exposure
ASOS clarified that the incident potentially exposed basic personal details such as names and contact information. However, the company emphasized that payment card data and account credentials were not compromised. The exact number of affected users remains undisclosed, though the breach raised concerns about the scale of potential data exposure.
Attackers claim access to Snowflake instance
A screenshot of the notification, shared by a user on a public forum, revealed that the message was directed at ASOS’s data protection officer and IT team. The attackers stated, “We have fully compromised the Snowflake instance. Engage with us, or we will leak it,” followed by a link to a Telegram channel. This channel is associated with a previously unidentified threat group named Xuanye Group.
According to reports from Reuters, the group asserted that payment information was not affected and that the ASOS app remained secure for use. They also indicated that customer data stored on their servers would remain untouched for a specified duration.
Snowflake investigation ongoing
Snowflake, the cloud data platform utilized by ASOS for analytics and storage, confirmed that its investigation is ongoing. The company stated that no evidence of compromise has been found to date.
Expert analysis highlights potential risks
Pieter Arntz, a senior malware intelligence researcher at Malwarebytes, noted that the breach’s scope remains unclear but emphasized the significance of the connection between ASOS and Snowflake. “ASOS employs Simon AI for marketing, which operates on Snowflake’s infrastructure. While the link is indirect, any exposure could reveal detailed customer profiles, including browsing behavior, purchasing patterns, location data, and loyalty metrics. This information holds substantial value for malicious actors,” he explained.
Alan Snyder, CEO at NowSecure, highlighted the broader implications of mobile app security. “The mobile application serves as the primary interface for customer interactions and transactions. A compromise could enable attackers to mimic legitimate customer service communications, such as fraudulent payment requests. This underscores the necessity for retailers to rigorously monitor and control access to messaging systems and connected services,” he stated.
Broader context of cyberattacks
The incident aligns with a series of cyberattacks targeting UK-based retailers in 2025, including Marks Spencer, the Co-op, and Harrods. Security professionals have reiterated the importance of proactive measures to safeguard customer data and maintain trust in digital platforms.
“We have fully compromised the Snowflake instance. Engage with us, or we will leak it,” followed by a link to a Telegram channel.

About Author

 English