

Ghaziabad Man Arrested for Credit Card Fraud via Cloud Kitchens
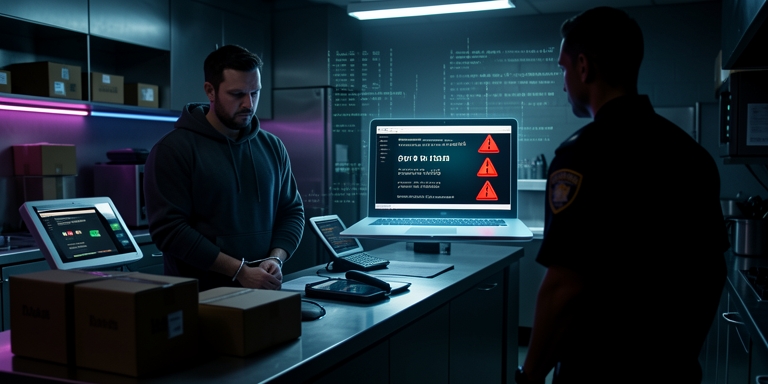
Ghaziabad Police Crime Branch has detained a 21-year-old individual for allegedly orchestrating a financial fraud scheme involving stolen credit card information and fraudulent food delivery transactions.
The Fraud Scheme
The suspect, identified as Satyavrat, is accused of exploiting a network of cloud kitchens to siphon funds from victims through unauthorized transactions. The operation reportedly involved the acquisition of sensitive customer data from a former banking role. Investigators stated that Satyavrat accessed details of approximately 52 clients from a private financial institution by leveraging a messaging application group. He then impersonated a bank representative to extract credit card numbers and one-time passwords (OTPs) during deceptive phone calls.
Data Breach and Social Engineering
The stolen financial information was utilized to generate fictitious food orders through cloud kitchens under his control. Payments for these orders were processed using victims’ credit cards, with the proceeds funneled through the food delivery platform to the accused. This method enabled the diversion of funds from compromised accounts into the suspect’s possession.
Impact and Arrest
Complaints from affected customers led to the removal of two cloud kitchens linked to the scheme. However, Satyavrat allegedly established a third outlet to continue the activity. Police estimates indicate that victims lost over ₹30 lakh over a seven- to eight-month period. A recent incident on September 17 involved the theft of ₹38,000 from a Ghaziabad resident, prompting the food delivery platform to file a formal complaint.
Investigation and Arrest
Law enforcement officials traced the suspect’s activities to the Kaushambi area, where he was apprehended. Ongoing investigations focus on verifying the scope of the fraud, including the verification of transaction records, digital communication channels, and financial accounts associated with the cloud kitchens. Authorities are also examining the source of the initial customer data breach, particularly how information from the former bank was accessed through the messaging application group.
Security Vulnerabilities and Advice
The case highlights vulnerabilities in data security and the risks of social engineering tactics.
The investigation remains active to determine the full extent of the fraud and identify any additional affected parties.
About Author

 English