

Tuskira Vector: Autonomous Red Teaming for Advanced Attack Surface Validation
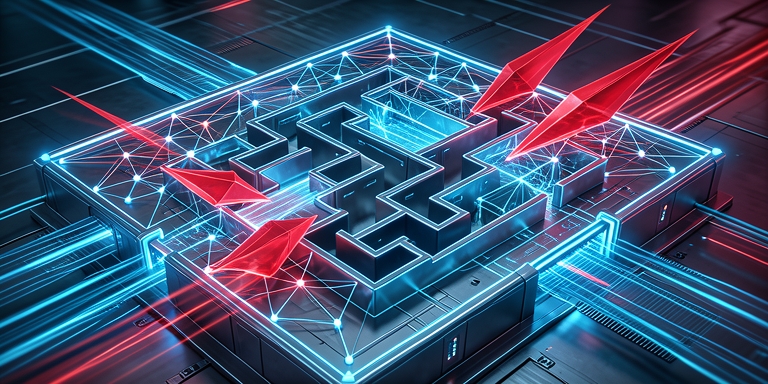
Tuskira’s Vector is an autonomous red teaming solution that simulates external adversary behavior to assess and validate an organization’s attack surface.
Introduction to Vector
Tuskira has introduced Vector, an autonomous red teaming solution designed to assess and validate an organization’s attack surface by simulating external adversary behavior. The platform leverages advanced threat intelligence, emerging tactics, techniques, and procedures (TTPs), and AI-driven methodologies to probe approved external attack surfaces. It cross-references findings against an organization’s existing security controls, internal risk data, and infrastructure configurations to identify actionable threats.
How Vector Works
Red Team Agent
The Red Team Agent operates by analyzing internet-facing assets, services, identities, and misconfigurations across hybrid environments, including cloud, identity, endpoint, network, and on-premises systems.
Security Data Fabric
Vector utilizes Tuskira’s Security Data Fabric, which aggregates and normalizes data from third-party security tools into a dynamic digital twin of the enterprise. This framework provides real-time visibility into security architecture, application topologies, deployed controls, and reported risks.
Key Capabilities
Vector’s key capabilities include continuous adversarial validation of vulnerabilities, identities, and control configurations, allowing security teams to proactively address threats. The platform streamlines incident response by automatically attaching contextual details—such as asset ownership, identity relationships, and potential blast radius—to validated attack paths. Additionally, it recommends immediate control adjustments, such as modifying firewall rules, IAM policies, or EDR settings, and retests to confirm mitigations.
CEO Statement
Piyush Sharrma, CEO of Tuskira, emphasized that while organizations often know what is exposed, they lack clarity on whether attackers can exploit these weaknesses. Vector bridges this gap by simulating external attacks and cross-referencing results with internal security data, enabling teams to resolve issues through control adjustments rather than waiting for patch cycles.
Expansion on Kairo Platform
The release expands on Tuskira’s Kairo platform, introduced in May 2026, which identifies cross-domain breach paths and validates them against existing defenses. New features include red team sensors that maintain an up-to-date threat model without scheduled engagements and an agentic defense loop that automates prioritization, investigation, and verification.
Components and Integration
Collaborative Tools
Components like Kairo, Lattice, Quell, and Iris work in tandem to map attack paths, validate exposures, assess newly disclosed vulnerabilities, and investigate alerts with contextual data.
Deployment Impact
In deployments, Kairo has reduced the volume of scanner findings by up to 99% by identifying unreachable threats and recalculating breach paths as environments evolve. This allows security operations teams to focus on exploitable weaknesses, insufficiently detected risks, or poorly controlled exposures.
Proactive Cybersecurity Vision
Tuskira’s solution aims to shift cybersecurity from reactive to proactive defense by integrating continuous threat simulation with enterprise-specific data, ensuring organizations address the most critical risks efficiently.

About Author

 English