

Understanding Cloud Entitlement Risk: Impact on Executive Cloud Security Strategies
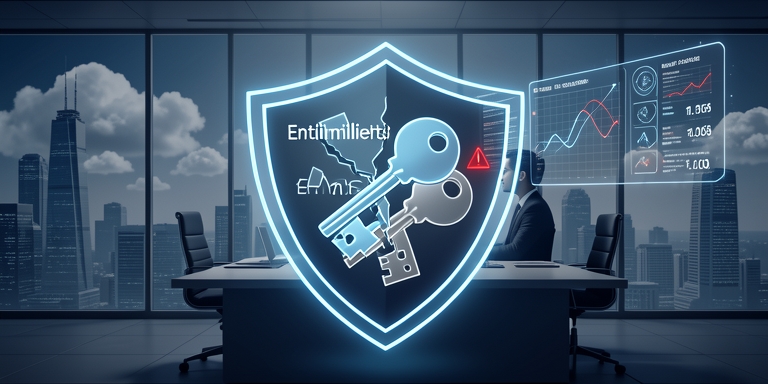
Cloud security investments often fail to achieve their intended risk reduction when organizations lack clarity on the actual capabilities of their cloud identities in the event of a breach.
The Core Issue
Cloud entitlement risk arises from the mismatch between leadership’s understanding of what cloud identities can do and the permissions those identities actually hold.
This gap is prevalent across cloud environments due to factors like rapid development cycles, template-based deployments, and service account provisioning, which often result in permissions exceeding operational needs and accumulating over time. Leadership may have approved security investments without recognizing this gap or its scale.
The risk extends beyond compromised high-privilege identities.
A more insidious threat involves low-privilege identities that can silently escalate privileges through permissive role assumption policies, overly broad IAM write permissions, or unreviewed cross-account trusts. These escalation paths are typically hidden in policy documentation and often overlooked during manual access reviews.
Organizational Impact
The inability to answer these questions directly translates to board-level financial and operational consequences. Breach scope expands with the breadth of cloud permissions, and compromised credentials remain the leading initial breach vector, according to the IBM report. While the report does not explicitly link breach costs to permission scope, the implications are clear: the permissions associated with compromised credentials, not just the credentials themselves, dictate the financial and operational impact of a breach.
Industry Practices
Mature cloud entitlement programs, often implemented through CIEM platforms or equivalent tools, enable organizations to generate verified permission reports for any cloud identity on demand. These programs include quarterly reviews of high-risk identities and unused permissions, with documented evidence of reductions. They maintain visibility into privilege escalation paths, not just static permissions, and can provide historical access snapshots to incident responders.
Strategic Decisions
Leadership faces two interconnected investment choices. First, establishing verified visibility into what cloud identities can actually do—effective permissions rather than granted policies. This is a prerequisite for all other cloud security decisions. Without it, organizations cannot assess breach blast radius, identify escalation paths, prove entitlement state to auditors, or accurately scope cloud incidents.
Key Questions
- What actions can every cloud identity, including service and automation accounts, perform if compromised?
- Which identities have the ability to alter security controls, disable logging, or create new privileged access?
- What would an attacker with access to the highest-privilege identity be able to access, modify, or destroy?
- Can the organization provide evidence of its current cloud entitlement state for regulators, auditors, or incident responders within hours?
- When were the permissions for cloud service identities last reviewed and validated against operational requirements?
Sources
IBM Cost of a Data Breach Report 2024
About Author

 English