

WhatsApp Scam: ₹1.40 Crore Lost, Four Arrested in Bengaluru
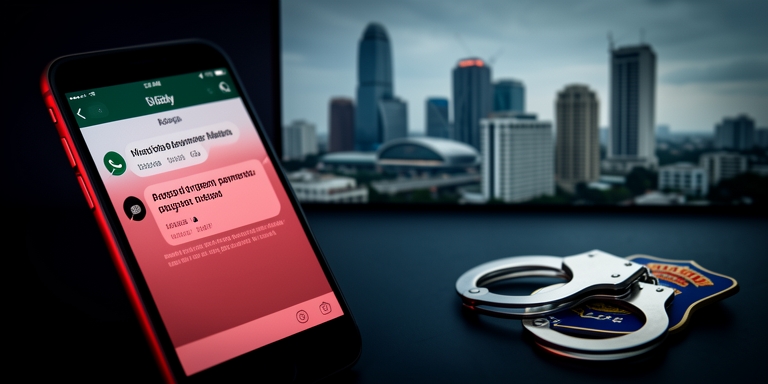
Karnataka Cyber Command has detained four individuals in connection with a ₹1.40 crore financial fraud involving the impersonation of a university administrator.
The Fraud Scheme
Karnataka Cyber Command has detained four individuals in connection with a ₹1.40 crore financial fraud involving the impersonation of a university administrator. The incident unfolded when unauthorized transactions were detected from an institution’s banking account, leading to a probe that uncovered a sophisticated scheme leveraging digital deception. Authorities recovered ₹8.50 lakh in cash and four mobile devices linked to the operation.
The Impersonation
The fraudulent activity began on September 8 when an accountant at a deemed university received a communication purportedly from the institution’s president. The sender utilized a photograph of Dr Chennaraj Roychand, the university’s head, to establish credibility. At approximately 10:03 am, the impersonator inquired about the institution’s financial balance. Believing the request originated from the president, the accountant engaged in the conversation.
Digital Exploitation
Later that day, at 11:34 am, the fraudster instructed the transfer of ₹1.40 crore through a messaging platform, which the accountant executed without verification. This case exemplifies a “boss scam,” a tactic where cybercriminals mimic senior executives to manipulate employees into transferring funds or disclosing sensitive data. The scheme relied on the accountant’s trust in the perceived authority of the sender, bypassing standard verification protocols.
Investigators noted that the fraudster likely exploited the university’s internal communication systems to gather contextual details, enhancing the authenticity of the deception. A thorough investigation revealed that the perpetrators had accessed institutional data by distributing a ZIP file containing malicious content. Analysis indicated that opening the file via the Chrome browser allowed unauthorized access to internal systems, enabling the theft of financial information.
Investigation and Arrests
The gang reportedly monitored the university’s transactions for 15–20 days prior to executing the transfer, suggesting premeditated planning. Foreign IP addresses were also linked to the operation, complicating the tracing of digital footprints. Four suspects were arrested following forensic analysis of the financial trail. Annayya, 25, from KR Puram in Bengaluru, Rupasali Ravikumar Reddy, 26, and Ambaraya, 39, were detained in Hyderabad, while Syed Wajihuddin Quadri, 25, was apprehended in connection with cash collection.
Recovery and Forensic Analysis
Police confirmed that the group coordinated multiple roles, including account acquisition, fund transfers, and cash withdrawals. A fifth individual, Sunny alias David, remains at large, with ongoing efforts to locate him. The stolen funds were allegedly funneled through a network of compromised bank accounts. Sunny is alleged to have recruited acquaintances to open accounts in exchange for financial incentives, which were then used to receive and redistribute the illicit proceeds.
Cybersecurity Lessons
Hyderabad-based suspects were reportedly positioned to collect the transferred money via cheques, which were later converted into cash. This multi-layered approach aimed to obscure the source of the funds and evade detection. During the investigation, law enforcement recovered ₹8.50 lakh in cash, linked to a separate fraud case in Aurangabad, Maharashtra. Digital evidence, including messaging records and banking transactions, was analyzed to map the operation’s structure.
Preventive Measures
The case was managed under the supervision of Cyber Command DGP Pranab Mohanty, with collaboration from cybercrime units in the South Division. To mitigate similar risks, cybersecurity authorities advise employees to independently verify requests from senior officials, particularly those involving financial transactions. They emphasized that messages containing official photographs should not be automatically accepted as genuine. Employees are urged to confirm such instructions through separate, verified communication channels.
Additionally, warnings were issued against opening suspicious ZIP files or sharing bank account details for monetary gain. The incident underscores the vulnerabilities of organizational systems to social engineering attacks. The perpetrators combined identity theft, digital exploitation, and financial laundering to execute the fraud, highlighting the need for robust verification processes and employee training.
Conclusion
Institutions are encouraged to implement multi-factor authentication, monitor transaction patterns, and conduct regular cybersecurity audits to prevent unauthorized access. Organizations are also advised to establish clear protocols for financial transfers, ensuring that no transaction is authorized solely based on digital communications. In the event of suspected fraud, immediate reporting to the national cybercrime helpline (1930) is critical to initiating rapid response measures. The case serves as a stark reminder of how a single deceptive message can compromise an entity’s financial integrity, necessitating heightened vigilance and proactive safeguards.
About Author

 English