

AI-Powered Cybercrime Threat: New Zealand Experts Warn of Rising Risks
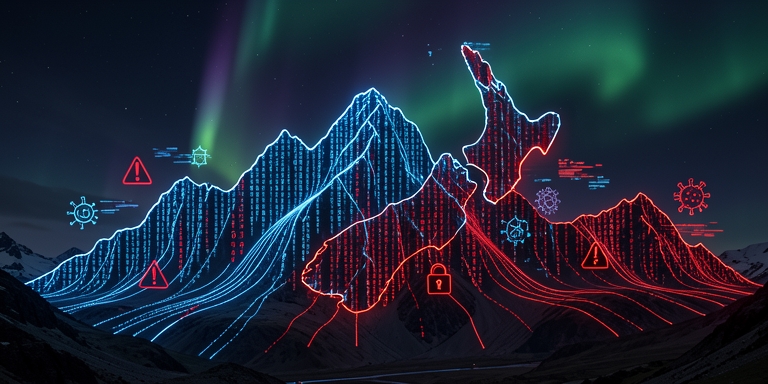
New Zealand’s National Cyber Security Centre (NCSC) has issued a caution to businesses and leaders about AI-driven cybercrime, highlighting its role in reshaping cybersecurity threats.
NCSC’s Caution on AI-Driven Cybercrime
The National Cyber Security Centre (NCSC) of New Zealand has issued a caution to businesses and organizational leaders, highlighting that artificial intelligence is transforming the cybersecurity landscape by enabling faster, more scalable, and potentially personalized attacks. The agency emphasized that AI is not merely an emerging tool but a force reshaping the threat environment, with malicious actors leveraging its capabilities to automate operations, identify vulnerabilities, and refine targeting strategies.
Key Concerns
The NCSC outlined several critical areas of concern. It noted that AI is already integrated into criminal toolkits, with applications in phishing campaigns, scams, and social engineering attacks. These methods are becoming more convincing and credible, lowering barriers for attackers while increasing the sophistication of fraudulent activities. The agency warned that future AI models could automate threat execution, detect system weaknesses, and enable hyper-personalized targeting of both organizations and individuals.
Rising Cyber Incidents
Recent data from the NCSC revealed a significant rise in cyber incidents. During the 2025-26 period, the agency addressed 369 incidents of potential national significance, representing a 16.2% increase compared to the prior year. Four of these incidents were classified as C2, or Highly Significant, a figure matching the total recorded over the previous decade. The agency attributed this trend to evolving cybercrime economics, with attackers adopting more persistent and aggressive tactics to extract payments through extortion and data theft.
Specific Threats and Risks
Beyond financial losses, the NCSC highlighted the broader risks of personal data breaches, which can lead to secondary criminal activities affecting individuals. A specific threat identified by the NCSC involves North Korean operatives seeking remote IT employment. The agency reported cases where individuals clandestinely secured remote positions with New Zealand businesses to generate foreign currency for the North Korean state. Such activities violate United Nations sanctions and pose compliance, security, and espionage risks. The NCSC warned that these operations could also facilitate extortion attempts against targeted organizations.
NCSC’s Advice on Cybersecurity Practices
Despite the growing AI-driven risks, the NCSC stressed that foundational cybersecurity practices remain the most effective defense. It advised organizations to maintain a dual approach combining human-led and AI-enhanced threat detection. The agency emphasized that basic security measures must be regularly updated rather than assuming AI necessitates entirely new protective strategies. Weaknesses in fundamental practices, it noted, continue to provide entry points for attackers regardless of technological advancements.
Leadership and Governance
The NCSC urged boards and senior leadership to treat cybersecurity as a governance priority. It recommended that executives evaluate whether their organizations possess the personnel, processes, and resources to address a rapidly evolving threat environment. The agency acknowledged the difficulty of preparing for every possible cyber threat but emphasized the importance of proactive leadership in mitigating risks associated with AI.
Quotes and Key Takeaways
Catriona Robinson, head of the NCSC, stated that government cannot shield all organizations from cyber threats, underscoring the responsibility of individual entities to manage their security postures. She highlighted that organizations preparing for AI-driven challenges will be better equipped to navigate the complexities of emerging technologies.
The NCSC’s analysis underscores that AI is not creating a distinct category of cybercrime but amplifying existing techniques such as phishing, social engineering, and targeted attacks. For enterprises, the key takeaway is that advanced security technologies alone are insufficient. Strengthening core cybersecurity fundamentals, establishing clear accountability at the executive level, and investing in resources to counter automated threats remain critical to managing evolving risks.
About Author

 English