

Evooo1Bot Linux Botnet Exploits Routers as Traffic Relay Nodes
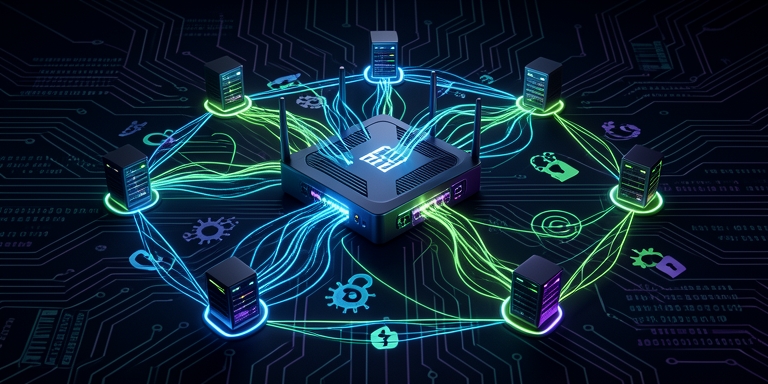
A newly identified Linux-based botnet named Evooo1Bot has emerged as a threat to internet-facing gateway devices, transforming them into SOCKS5 traffic relay nodes.
Evooo1Bot Overview
This malware, derived from the Mirai framework, exhibits advanced capabilities including credential harvesting, SSH brute-force attacks, and distributed denial-of-service (DDoS) operations. Since July, the botnet has targeted devices from manufacturers such as Alcatel, NETGEAR, Tenda, Mitsubishi Electric, Telesquare, and D-Link across multiple regions by exploiting known vulnerabilities.
Exploitation Techniques
Evooo1Bot leverages the DDoS engine from the publicly disclosed Mirai source code but enhances it with additional functionalities. These include encrypted command-and-control (C2) communications, an SSH brute-force scanner, a SOCKS relay module, a credential interception tool, and an integrated exploit suite targeting various vulnerabilities.
Recent variants of the malware incorporate a dedicated module for exploiting weaknesses in Hikvision cameras, Atlassian Confluence servers, Zyxel firewalls, TP-Link routers, D-Link NAS devices, WSO2 applications, Kubernetes ingress-nginx components, and vulnerable PHP-CGI installations. However, some embedded exploits contain implementation flaws that result in failed attacks.
Persistence and Control
Upon successful exploitation, Evooo1Bot establishes encrypted C2 connections over port 443 and performs extensive checks to detect debugging tools, security software, sandboxes, virtual machines, containers, and honeypots before executing its payload. Persistence mechanisms include systemd, SysV init, shell profiles, and rc.local configurations, while a cron job attempts to maintain access.
The malware features an interactive shell for remote control, enabling file transfers and command execution. A credential sniffer module monitors system processes to capture HTTP Basic Authentication credentials and cookie headers from /proc/net/tcp. The SOCKS5 module supports both direct listening and reverse-relay modes, allowing attackers to mask malicious traffic, bypass geographic restrictions, or infiltrate networks via compromised systems.
DDoS and Attack Vectors
Multiple simultaneous proxy sessions can be initiated, creating opportunities for monetization through residential proxy services if the botnet scales significantly. The SSH scanner employs 150 predefined username-password combinations for enterprise accounts and includes post-login checks to evade honeypots. The DDoS module, inherited from Mirai, supports 16 attack vectors, including UDP, DNS, SYN, ACK, GRE, fragmented TCP, and HTTP floods with customizable request parameters.
Mitigation Strategies
To mitigate risks, organizations are advised to ensure firmware updates for IoT devices, replace default administrative credentials, disable remote access interfaces, and replace hardware when vendors cease support. Research indicates that 37% of malicious activities are blocked when valid credentials are compromised.
The Blue Report 2026 evaluates defensive measures across 338 million simulations in live environments.
Additional Coverage
Additional coverage includes emerging threats such as the Dysphoria DDoS botnet, malicious 7-Zip installers, and the AryStinger botnet’s impact on D-Link routers. Other developments highlight Google’s efforts to reduce unwanted Android notifications and the proliferation of fake Chrome VPN extensions routing traffic through proxies.
About Author

 English